
What Happened in the Ronin Bridge Hack?
In March 2022, attackers took over five of nine Ronin validator keys and stole about $620M in ETH and USDC. How it happened and what changed.
In the Ronin bridge hack, attackers stole 173,600 ETH and 25.5 million USDC, worth about $620 million at the time, from the bridge linking the Axie Infinity game’s Ronin network to Ethereum. The theft happened on March 23, 2022, and was not discovered until March 29. The FBI later attributed it to North Korea’s Lazarus Group.
What Ronin was
Ronin was a sidechain built by Sky Mavis, the company behind Axie Infinity, a blockchain game in which players bought, bred and battled digital creatures held as NFTs. At its height in November 2021, the game reported 2.7 million daily active users and $214 million in weekly trading of in-game NFTs. Ethereum’s main chain was too slow and expensive for that volume of small transactions, so Sky Mavis ran its own network and a bridge for moving ETH and USDC between Ethereum and Ronin.
The bridge was secured by nine validators. Any deposit or withdrawal needed signatures from five of them. That design, a multi-signature threshold, is common among bridges, and it puts enormous weight on a small number of keys. See what a cross-chain bridge is.
How the attackers got in
The breach began with a job offer. According to reporting by The Block, a senior Sky Mavis engineer was approached on LinkedIn by a company that did not exist. After several rounds of interviews, he was offered a job with an unusually generous package, delivered as a PDF. The document carried spyware, and opening it gave the attackers a foothold inside Sky Mavis’s systems. Sky Mavis later said its staff faced constant spear-phishing attempts across social channels and that one employee had been compromised.
From there, the attackers reached the validator nodes and took control of the four validators Sky Mavis ran itself. They needed one more signature.
The forgotten permission that provided the fifth key
The fifth signature came from an arrangement made months earlier. In November 2021, as traffic surged, Sky Mavis asked the Axie DAO, the community organization that ran one of the validators, for help handling the load. The DAO allowlisted Sky Mavis to sign transactions on its behalf. That arrangement ended in December 2021, but the allowlist access was never revoked. Once inside Sky Mavis’s systems, the attackers could use it, through a gas-free RPC node the company operated, to obtain the Axie DAO validator’s signature.
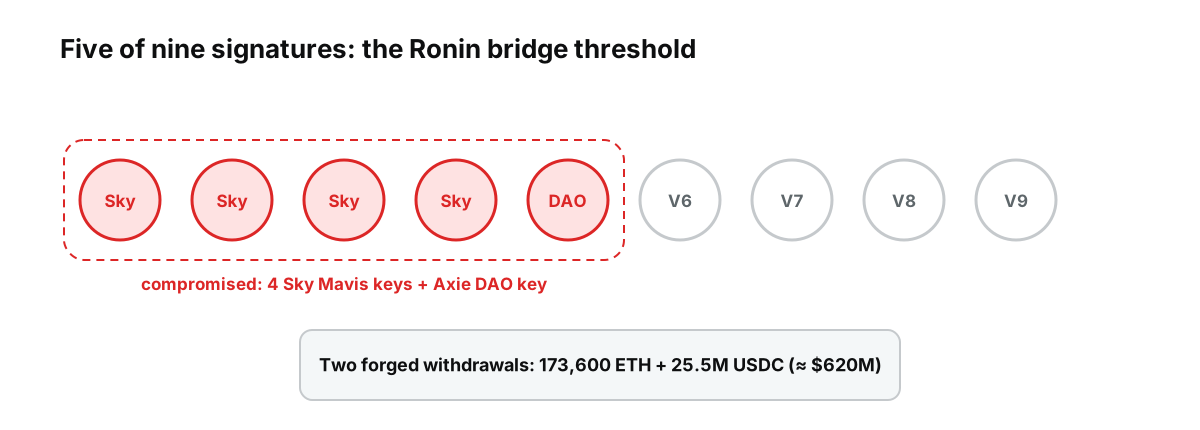
Figure: Five of nine signatures were enough. Four Sky Mavis keys plus the Axie DAO validator gave the attacker the threshold.
That gave them five signatures: four Sky Mavis keys plus the Axie DAO key, exactly the threshold. With them, they approved two withdrawals that drained the bridge of 173,600 ETH and 25.5 million USDC.
Timeline
| Date | Event |
|---|---|
| November 2021 | Axie DAO allowlists Sky Mavis to sign on its behalf during a traffic surge |
| December 2021 | The arrangement ends, but the allowlist access is not revoked |
| March 23, 2022 | Two forged withdrawals drain the bridge |
| March 29, 2022 | Theft is discovered when a user cannot withdraw 5,000 ETH; Sky Mavis halts the bridge and the Katana exchange |
| Early April 2022 | Sky Mavis raises $150 million from investors, including Binance, to reimburse users |
| April 2022 | The FBI attributes the attack to the Lazarus Group; the US Treasury sanctions an address linked to the hack |
| Late April 2022 | Ronin announces an expanded validator set, from nine to eleven |
| June 28, 2022 | The bridge reopens with a revised design |
| September 2022 | Law enforcement recovers about $30 million of the stolen funds |
| February 2023 | A further $5.8 million is recovered |
At the time it was the largest crypto theft on record, ahead of the roughly $611 million taken from Poly Network in August 2021.
Why it went undetected for six days
The withdrawals looked valid to the bridge because they carried the required signatures. Nothing in the system flagged that five keys had signed in an unusual pattern, and monitoring did not catch that the bridge’s balance had been drained. Only when a user’s legitimate withdrawal failed did the team investigate.
The delay mattered. It gave the attackers six days to start moving and laundering funds before exchanges and analysts could react, which is one reason so little was ever recovered.
What it meant for Axie players
For ordinary users, the most immediate effect was that their funds were stuck. With the bridge and the Katana exchange halted, assets on Ronin could not be moved back to Ethereum for three months, until the bridge reopened at the end of June 2022. Sky Mavis committed to reimbursing users from the $150 million it raised and from its own balance sheet, so players did not ultimately bear the theft directly. But the episode arrived as the game’s activity was already falling, and confidence in play-to-earn games took a lasting hit.
A second incident, and a design lesson applied
The bridge was hit again in August 2024, when a recent update introduced a flaw in how it counted the votes needed to approve withdrawals. White-hat hackers exploited it, withdrew 4,000 ETH and 2 million USDC, about $12 million, and returned it. The amount was capped because the bridge by then limited how much could leave in a single transaction, a safeguard of exactly the kind the 2022 hack had shown to be missing.
What the Ronin hack taught the industry
A multisig is only as strong as the separation between its keys. Nine validators sounded decentralized, but one organization controlled four keys and had standing access to a fifth.
Old permissions are live risk. A temporary arrangement that nobody remembered to switch off provided the final key. Access reviews matter as much as encryption.
People are the attack surface. The attackers did not break any cryptography. They persuaded one engineer to open one document. Fake job offers have since become a familiar tactic against crypto companies, and security teams now train staff to treat unsolicited recruitment approaches with the same suspicion as phishing emails.
Bridges need limits and monitoring, not just signatures. Caps on withdrawals, delays on large transfers and alerts on unusual signing patterns turn a catastrophic loss into a contained one.
Users carry bridge risk without seeing it. Players holding assets on Ronin depended on the bridge’s security, whether they understood the design or not. See layer 1 vs layer 2 blockchains for how different designs inherit, or do not inherit, the security of the chain they connect to.
Attribution is not recovery. Naming the attackers and sanctioning their addresses did not bring most of the funds back. See why blockchains are not anonymous for how stolen funds are traced, and why tracing and recovering are different things.
How to judge a bridge before using it
The questions Ronin’s users never asked are the ones worth asking of any bridge:
- Who signs withdrawals, and how many signatures are needed? A handful of keys controlled by one company is a single point of failure, whatever the headline number.
- Are the signers genuinely independent? Separate organizations, infrastructure and security teams matter more than the count.
- Are there withdrawal caps and delays? Limits on how much can leave at once cap the damage from any breach.
- How much value is locked? The more a bridge holds, the more attractive a target it becomes.
- What is its track record? Audits, bug bounties and how past incidents were handled say a lot about how seriously security is taken.
For moving assets you intend to hold for a long time, the safest bridge is often the one you do not need: keeping assets on the chain where they were issued avoids bridge risk entirely. For the wider context, see what Web3 is and what blockchain is.
This article is educational content and does not constitute financial, investment, legal or tax advice. Digital assets are volatile and you may lose the amount you invest.
Sources
- $620 Million in Crypto Stolen From Axie Infinity’s Ronin Bridge — BleepingComputer, March 29, 2022
- Axie Infinity Ronin Network Hack (discovery, reimbursement funding, FBI attribution) — BitPinas, 2022
- US Authorities Link $600m Cryptocurrency Theft to North Korean Lazarus Group (OFAC listing) — Computing, April 2022
- Ronin Network Reveals New Validators Count and Relaunch Date After $620M Hack — CryptoPotato, April 2022
- Hackers used fake job offer to hack and steal $540 million from Axie Infinity (LinkedIn offer, spyware PDF; Sky Mavis post-mortem; bridge relaunched in June) — The Hacker News, July 2022
- An elaborate LinkedIn scam led to one of the largest heists in crypto history (Axie DAO allowlist November 2021, discontinued December 2021 but not revoked) — TechRadar
- How did the Ronin bridge hack take place? (bridge reopened June 28, 2022; 2.7 million active users and $214 million weekly NFT volume in November 2021) — eGamers
- Ronin Network hacked, $12 million returned by white hat hackers (August 2024; $30 million recovered September 2022 and $5.8 million February 2023) — BleepingComputer, August 2024